WebSockets vulnerabilities

WebSockets is an advanced technology that allows you to open an interactive two-way connection between a user’s browser and a server. Unlike a traditional HTTP request, which follows a request-response model and closes the connection after data transfer, WebSockets maintain a persistent connection, allowing both parties to exchange data in real time with minimal latency.
Popular WebSockets vulnerabilities
WebSocket servers should validate the
Originheader in the HTTP upgrade request to ensure the request comes from a trusted source. Failure to properly validate this can lead to Cross-Site WebSocket Hijacking (CSWSH), allowing attackers to initiate malicious WebSocket connections.By default, WebSocket connections are not encrypted, making them vulnerable to data interception. Using unsecured WebSocket connections (
ws://instead ofwss://) can lead to the exposure of sensitive information.WebSocket connections often rely on the same authentication and session management mechanisms as regular HTTP sessions, which can lead to vulnerabilities related to session hijacking and other session management attacks.
WebSocket connections consume significant server resources, and an attacker could attempt to exhaust these resources by establishing a large number of connections, leading to a denial of service for legitimate users.
If a web application using WebSockets does not properly sanitize input data, an attacker could inject malicious code (such as JavaScript) that executes in the user’s browser. This could lead to Cross-Site Scripting (XSS) through WebSocket connections.
Bugs in software or misconfigurations of the server handling WebSocket connections can introduce additional vulnerabilities, such as arbitrary code execution or bypassing access controls.
Examples of exploitation
To better understand WebSocket vulnerabilities, let’s examine a scenario from a web security lab. This particular lab challenges participants to exploit WebSocket vulnerabilities within a web application’s chat feature.
The chat is designed to allow real-time communication between users and a support agent through WebSocket messages. The objective is to manipulate the WebSocket messages to trigger a alert() popup on the support agent’s browser, demonstrating the potential for executing arbitrary JavaScript if the WebSocket messages are not properly sanitized by the application. This kind of exploit could be an instance of a Cross-Site Scripting (XSS) attack facilitated through WebSocket communication.
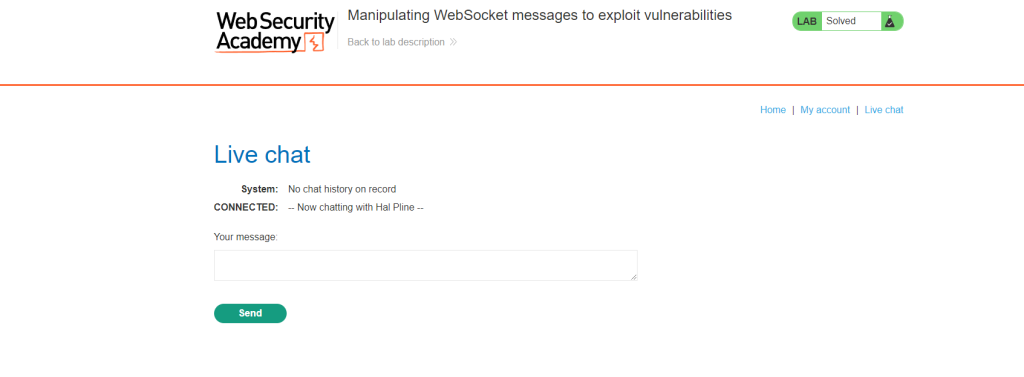
Let’s take a look at the live chat functionality.

We see 1 field to which we can send something. Let’s send a message and intercept the request with burp. When sending a message as <> we see that it was encoded in HTML before sending.

Let’s change our message right in the request!

Now let’s submit this request and go to the web page. As we can see our XSS was successful!

Scanners that detect vulnerabilities
OWASP ZAP (Zed Attack Proxy): This is a free, open-source penetration testing tool for finding vulnerabilities in web applications. It has WebSocket support and can be used to manually or automatically find security issues.
Burp Suite: This integrated platform for performing security testing of web applications includes tools for testing WebSockets. Burp Suite can intercept, inspect, modify and replay WebSocket messages.
WebSocket-Node: This is a WebSocket client and server implementation for Node.js. It can be used in combination with other tools to script custom tests for WebSocket services.
Wireshark: While not a vulnerability scanner per se, Wireshark can capture WebSocket traffic when configured correctly. It can be used to analyze the WebSocket handshake and subsequent data transfer for potential issues.
wssip: This application acts as a man-in-the-middle proxy that captures WebSocket communications between the client and the server. It allows you to manipulate WebSocket messages on the fly, which can be useful for testing how the server responds to unexpected input.
websocket-extensions: This is a Node.js library that can be used to build custom tools for testing WebSocket extensions. It can be used to test the server’s handling of various WebSocket extension negotiation scenarios.
nmap with NSE scripts: Nmap is primarily a network testing tool, but it has a scripting engine that can be used to probe web services, including WebSockets, for vulnerabilities.
Average CVSS score for WebSockets vulnerabilities
The average CVSS score for vulnerabilities related to Denial of Service (DoS) attacks via WebSockets can vary widely depending on the specific nature of the vulnerability and the impact it has on the affected system. Generally, DoS attacks via WebSockets are considered to have a high severity score due to the significant impact they can have if successfully executed. The CVSS score for a vulnerability is influenced by several factors, including how easily it can be exploited, the availability of any mitigations, the effects on system availability and data integrity, and the potential scale of an attack.
While there isn’t a specific average score provided for WebSocket vulnerabilities, it’s important to understand that the CVSS framework rates vulnerabilities on a scale from 0 to 10, with higher scores indicating more severe security risks. Each vulnerability will have its own CVSS score, which reflects its unique characteristics and potential impact.
For more detailed information on CVSS scoring for specific WebSocket vulnerabilities, one would need to consult a database of vulnerabilities, such as the National Vulnerability Database (NVD) or other security advisories that provide CVSS scores for individual Common Vulnerabilities and Exposures (CVEs).
CVES related to WebSockets vulnerabilities
• CVE-2021-42340: Apache Tomcat vulnerability causing a DoS due to a memory leak.
• CVE-2021-33880: Python websockets issue leading to an HTTP basic auth timing attack.
• CVE-2021-32640: ‘ws’ module vulnerability in Node.js, where a regex can cause a Denial of Service.
• CVE-2020-36406: uWebSockets has a stack buffer overflow problem.
• CVE-2020-27813: Gorilla WebSocket suffering from an integer overflow issue.
• CVE-2020-24807: socket.io-file allows a bypass of file type restrictions.
• CVE-2020-15779: socket.io-file vulnerability allowing path traversal.
• CVE-2020-15134: faye-websocket lacks proper TLS certificate validation.
• CVE-2020-15133: Similar to CVE-2020-15134, with faye-websocket not validating TLS certificates.
• CVE-2020-11050: Java WebSocket not performing SSL hostname validation.
To study WebSockets vulnerabilities
Familiarize yourself with the WebSocket protocol as defined in RFC 6455. Knowing how WebSockets work is crucial for understanding potential security issues.
Research common WebSocket vulnerabilities such as Cross-Site WebSocket Hijacking (CSWSH), Denial of Service (DoS) attacks, and payload manipulation.
Use virtual machines or containers to set up a safe environment where you can experiment with WebSocket communications without risking real systems.
Employ penetration testing tools like OWASP ZAP or Burp Suite to discover and exploit vulnerabilities in WebSocket implementations.
Follow the latest security research through advisories, CVE databases, and security blogs that focus on WebSockets.
Review the source code of open-source WebSocket implementations to understand how they handle security and where they might go wrong.
Re-create known WebSocket exploits in your lab to understand how attackers exploit these vulnerabilities.
Engage with online security communities and contribute to discussions on WebSocket security.
Engage with interactive labs from platforms like Portswigger’s Web Security Academy, Hack The Box, and TryHackMe, which offer scenarios involving WebSocket vulnerabilities to provide practical, hands-on experience.
How to be protected from WebSockets vulnerabilities
Use WebSocket Secure (WSS), which incorporates TLS/SSL encryption, to safeguard data in transit against eavesdropping and tampering.
Rigorously validate all input on the server side to prevent injection attacks, such as Cross-Site Scripting (XSS) and SQL injection, which could exploit WebSocket messages.
Ensure that WebSocket connections are properly authenticated and that users are authorized to perform actions, preventing unauthorized access and actions within the application.
Implement rate limiting on WebSocket connections to protect against Denial of Service (DoS) attacks that could overwhelm the server by creating too many connections or sending too much data.
Manage WebSocket sessions carefully, ensuring they are securely established, maintained, and terminated to prevent session hijacking and other session-related attacks.
Keep all libraries, frameworks, and dependencies up to date to protect against vulnerabilities that have been discovered and fixed in newer versions.
Use security testing tools and practices, such as vulnerability scanners and penetration testing, to identify and remediate potential vulnerabilities in WebSocket implementations.
Conclusion
In an era where interactive web applications are becoming the norm, WebSocket technology plays a pivotal role in providing seamless bidirectional communication between clients and servers. However, as demonstrated by vulnerability analyses and practical exploits, security concerns are intrinsic. WebSocket vulnerabilities can have serious implications, including unreliable authentication, data interception, DoS attacks, and arbitrary code execution, potentially jeopardizing user data confidentiality, integrity, and availability.
Recognizing and acknowledging these vulnerabilities is the first step toward mitigating them. Developers and system administrators must actively employ encryption methods such as WSS, enforce strict input validation policies, authentication, and authorization, as well as implement strategies to protect against DoS attacks and code injections.
Diligent testing and monitoring using specialized tools like OWASP ZAP and Burp Suite, along with integrating security standards and practices into web application development and maintenance, ensure the detection and timely remediation of vulnerabilities. Moreover, it is crucial to engage in communities and stay abreast of the latest security research to ensure that applications remain secure in an ever-changing digital landscape.
By following these recommendations and fostering a culture of continuous learning and improvement, we can ensure that web applications are not only functional and efficient but also secure for all users.
Other Services
Insomnia Security Scanner
AI-powered web application security scanner by CQR. Automated vulnerability discovery, exploit verification, and detailed reporting for modern applications.
Learn moreInfrastructure Protection by CRYEYE
Security audits via CryEye provide enterprise information security, protecting the entire infrastructure.
Learn morePenetration Testing
Find vulnerabilities across your entire business infrastructure before hackers do! At penetration testing consulting, we will select pentest methods and other custom cybersecurity recommendations for your business.
Learn moreSocial Engineering
Simulate real-world phishing, vishing, and pretexting attacks to measure and improve your team's security awareness and response capabilities.
Learn morePerformance Testing
All kinds of load and performance testing of your system from the CQR online security company.
Learn moreAI-Powered Vulnerability Assessment
Leverage artificial intelligence to discover, prioritize, and remediate vulnerabilities across your digital assets faster and more accurately than traditional scanners.
Learn moreCloud Security Audit (AWS / GCP / Azure)
Comprehensive security review of your cloud environments — IAM policies, network controls, data exposure, and misconfigurations across all major cloud platforms.
Learn moreDevSecOps Integration
Embed security into every stage of your CI/CD pipeline. Automated SAST, DAST, SCA, and secret scanning so vulnerabilities are caught before they reach production.
Learn moreAPI Security Testing
In-depth testing of REST, GraphQL, and SOAP APIs for authentication flaws, authorization bypasses, injection vulnerabilities, and data leakage risks.
Learn moreMobile Application Penetration Testing
Manual and automated security testing for iOS and Android applications — reverse engineering, runtime analysis, traffic interception, and backend API assessment.
Learn moreIoT Security Assessment
Evaluate firmware, communication protocols, cloud backends, and physical interfaces of IoT devices to identify vulnerabilities before attackers do.
Learn moreBlockchain & Smart Contract Audit
Formal verification and manual code review of smart contracts on Ethereum, Solana, and other chains. Detect reentrancy, overflow, and logic flaws before deployment.
Learn moreRed Team Operations
Advanced adversary simulation using real attacker TTPs (MITRE ATT&CK) to test your detection, response, and overall security posture under realistic conditions.
Learn moreThreat Intelligence & Monitoring
Continuous monitoring of threat feeds, dark web, and attacker infrastructure to provide actionable intelligence specific to your organization and industry.
Learn moreZero Trust Architecture Review
Assess and design your Zero Trust security model — identity verification, micro-segmentation, least-privilege access, and continuous validation controls.
Learn moreCompliance Consulting (PCI DSS / SOC 2 / GDPR)
Expert guidance to achieve and maintain compliance with major security frameworks. Gap analysis, remediation roadmaps, and audit-readiness support.
Learn moreDark Web Monitoring
Continuous surveillance of dark web forums, marketplaces, and breach databases for leaked credentials, sensitive data, or mentions of your organization.
Learn morePhishing Simulation & Awareness Training
Controlled phishing campaigns combined with interactive security awareness training to build a human firewall across your entire organization.
Learn moreSupply Chain Security Audit
Assess third-party vendor risks, open-source dependencies, and software supply chain integrity to prevent attacks like SolarWinds and Log4Shell.
Learn moreContainer & Kubernetes Security
Security review of Docker images, Kubernetes clusters, RBAC policies, network policies, and runtime configurations to harden your container infrastructure.
Learn moreWeb Application Firewall (WAF) Deployment
Professional WAF setup, rule tuning, and ongoing management to block SQL injection, XSS, CSRF, and other OWASP Top 10 threats in real time.
Learn moreBug Bounty Program Management
Full lifecycle management of your bug bounty program — scope definition, researcher coordination, triage, validation, and remediation tracking.
Learn moreOSINT Investigation Services
Open-source intelligence gathering on individuals, organizations, and infrastructure. Ideal for pre-engagement recon, fraud investigation, and competitive analysis.
Learn moreDigital Forensics & Incident Response
Rapid response to security breaches — evidence collection, malware analysis, attacker timeline reconstruction, and actionable remediation recommendations.
Learn more