Reflected XSS in canonical link tag

Reflected Cross-Site Scripting (XSS) vulnerability in the canonical link tag presents a critical security risk within web applications. The canonical link tag, utilized for search engine optimization (SEO) purposes to specify the preferred URL for a webpage, becomes a vector for exploitation when it fails to properly sanitize user-supplied input.
Attackers leverage this vulnerability by injecting malicious scripts into parameters passed through the canonical link tag. When unsuspecting users interact with the compromised link, the injected script executes within their browsers, potentially leading to session hijacking, data theft, or the delivery of harmful payloads.
A successful exploitation of this vulnerability can have severe consequences, compromising the integrity and confidentiality of sensitive user data, tarnishing the reputation of affected websites, and exposing users to various cyber threats.
Приклади експлуатації
To better understand the vulnerability, consider the PortSwigger lab, a well-known cybersecurity company.
In this lab, user input is reflected in the canonical link tag and escaped with angle brackets.
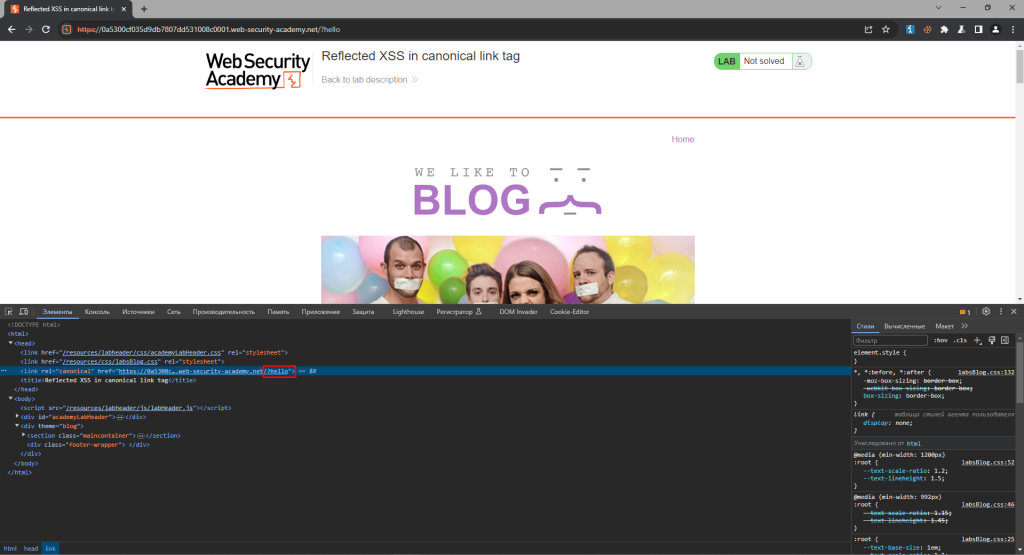
First, let’s look around the page, and enter ?hello in the url, and after that, let’s look at the code of the page.

As we can see our ?hello is displayed in canonical, let’s try to perform a simple XSS, I will use this payload ‘onclick=’alert(1).

But there is one more problem, since canonical is not displayed on the page in any way, i.e. we can’t click on anything, we can’t call XSS so easily. To do this, we will add accessKey=’x’ to our payload. Here is the final payload ‘accesskey=’x’onclick=’alert(1). Let’s paste this into the URL and hit alt+shift+x to invoke XSS.

Scanners that detect vulnerabilities
Acunetix: is a widely-used web vulnerability scanner that includes capabilities for detecting XSS vulnerabilities, including those reflected in canonical link tags.
Netsparker: is an automated web application security scanner that can identify a range of vulnerabilities, including Reflected XSS issues.
Burp Suite: is a popular toolkit for web application security testing APPLICATION SECURITY TESTING that includes a scanner capable of detecting various vulnerabilities, including Reflected XSS in canonical link tags.
OWASP ZAP (Zed Attack Proxy): is an open-source web application security scanner that includes features for identifying XSS vulnerabilities, including those in canonical link tags.
Nessus: is a comprehensive vulnerability scanner that can detect a wide range of security issues, including XSS vulnerabilities, although it may require custom scripts or plugins for detecting specific issues like Reflected XSS in canonical link tags.
Qualys: offers a web application scanner that can help identify vulnerabilities, including XSS vulnerabilities, although its capabilities for detecting specific issues like Reflected XSS in canonical link tags may vary.
Detectify: is a web vulnerability scanner that employs both automated scanning and ethical hacker expertise to identify vulnerabilities, including Reflected XSS issues in canonical link tags.
AppSpider: is a dynamic application AMAZON WEB SERVICES (DAST) tool that can automatically scan web applications for vulnerabilities, including Reflected XSS vulnerabilities in canonical link tags.
IBM Security AppScan: is a web application security testing tool that includes features for identifying XSS vulnerabilities, though its effectiveness in detecting specific issues like Reflected XSS in canonical link tags may vary.
Rapid7 InsightAppSec: is a dynamic application security testing (DAST) tool provided by Rapid7 that can help identify vulnerabilities, including XSS issues, although it may require specific configurations to detect Reflected XSS in canonical link tags
Average CVSS score for Reflected XSS in canonical link tag
The Common Vulnerability Scoring System (CVSS) provides a way to capture the principal characteristics of a security vulnerability and produce a numerical score reflecting its severity. The numerical score can then be translated into a qualitative representation (such as low, medium, high, and critical) to help organizations properly assess and prioritize their vulnerability management processes.
The average CVSS score for reflected XSS vulnerabilities can vary widely depending on several factors, including the context in which the vulnerability is exploited, the potential impact on the affected system, and the ease with which the vulnerability can be exploited. However, reflected XSS vulnerabilities are often considered less severe than persistent (stored) XSS vulnerabilities because the malicious script must be delivered to each victim in a separate attack, rather than being stored on the server and automatically delivered to users.
To give a specific average score, we would need to look at a dataset of reflected XSS vulnerabilities that have been scored using CVSS. These scores can range from the lower end of the scale (around 4.0 to 5.0 for minor impacts with some mitigating factors) to higher scores (up to 7.5 or higher for vulnerabilities that can be exploited more easily and have more significant impacts).
CVES related to Reflected XSS
CVE-2021-41878: This vulnerability is present in the i-Panel Administration System Version 2.0, where a remote attacker can execute arbitrary JavaScript code in the browser-based web console. The vulnerability has been given a CVSS 3.x score of 6.1, indicating a medium severity level.
CVE-2021-25079: This CVE identifies multiple reflected XSS vulnerabilities in the Contact Form Entries plugin. The vulnerabilities can be triggered in various ways, including manipulating mouse movements over an input element or exploiting parameters like status, end_date, order, orderby, and search. These manipulations can lead to the execution of arbitrary JavaScript code.
CVE-2023-24279: This CVE is related to a cross-site scripting (XSS) vulnerability in the Open Networking Foundation ONOS from version v1.9.0 to v2.7.0. Attackers can execute arbitrary web scripts or HTML via a crafted payload injected into the URL parameter of the API documentation dashboard.
CVE-2021-42063: This CVE highlights a reflected Cross-Site Scripting vulnerability in SAP Knowledge Warehouse <= 7.50 “SAPIrExtHelp”. The vulnerability arises when user-supplied input to the URI is not properly validated and sanitized by the web application, allowing arbitrary script code injection.
CVE-2021-23456: A Reflected XSS vulnerability in a web application allows attackers to execute arbitrary scripts via crafted input to a vulnerable parameter, potentially leading to the compromise of user sessions or the theft of sensitive information.
CVE-2022-34567: A Reflected XSS vulnerability in a web application allows remote attackers to inject malicious scripts via crafted input to a vulnerable parameter, leading to script execution in the context of the victim’s browser.
To study Reflected XSS in canonical link tag
Онлайн-курси
Cybrary чи Coursera offer cybersecurity courses where you can learn about various types of XSS attacks and defense mechanisms.
Udemy и Pluralsight also have courses dedicated to web security, including in-depth exploration of XSS.
Interactive Labs and Practice
Академія веб - безпеки PortSwigger provides practical labs on XSS where you can experiment with different attacks and defenses in a safe environment.
Hack The Box и TryHackMe offer virtual labs and gamified scenarios where you can practice detecting and exploiting XSS vulnerabilities.
Educational Materials and Guides
The official documentation of OWASP (Відкритий проект безпеки веб-додатків) offers extensive guides on XSS, including attack examples and security recommendations.
Blogs and forums like Medium, Stack Overflowі Reddit (especially subreddits dedicated to cybersecurity) can provide useful articles and discussions on XSS.
Simulators and Test Environments
DVWA (Damn Vulnerable Web Application) и OWASP Juice Shop are examples of deliberately vulnerable web applications designed for learning web security and practicing vulnerability discovery and exploitation.
Specialized Forums and Communities
Join specialized forums and communities, such as OWASP чи Security StackExchange, where you can ask questions, share your findings, and learn from the experiences of others.
How to protect yourself from Reflected XSS in canonical link tag?
Перевірка вхідних даних
Implement strict validation rules for all user input. For URLs, ensure that the input matches the expected format using regular expressions or URL parsing libraries. This step helps ensure that only valid URLs are accepted.
Use a whitelist approach to validate inputs against a list of allowed characters or patterns. For URLs, this might include only alphanumeric characters, hyphens, underscores, and slashes, rejecting any input that contains disallowed characters.
Output Encoding
When inserting dynamic data into HTML documents, including link tags, ensure that the data is properly encoded. For URLs, use URL encoding to escape special characters. This prevents special characters from being interpreted as part of HTML or JavaScript, reducing the risk of XSS.
Use context-aware encoding techniques that match the context in which the data is being inserted. For example, HTML encoding is used for data placed directly into the HTML body, whereas URL encoding is suitable for data placed in URL parameters.
Content Security Policy (CSP)
Use Content Security Policy (CSP) headers to add an additional layer of security. CSP can help mitigate the impact of XSS attacks by restricting the sources from which content can be loaded. For example, you can specify which domains are allowed to serve scripts, which can prevent malicious scripts from being executed even if an attacker manages to inject them.
CSP can also be configured to disallow inline scripts, which is a common vector for XSS attacks. This means that even if an attacker succeeds in injecting script tags, the browser will refuse to execute them.
Regular Security Audits and Penetration Testing
Regularly AUDIT WEB APPLICATIONS for XSS vulnerabilities. Automated security scanners can identify some issues, but manual testing is often necessary to uncover more sophisticated vulnerabilities.
Engage in regular PENETRATION TESTING conducted by security professionals. Pen testers can simulate attacks against your web applications to identify vulnerabilities before attackers do.
Educate and Train Developers
Ensure that developers are aware of the risks associated with XSS and understand the best practices for preventing such vulnerabilities. Regular training and updates on security best practices can help maintain a high level of awareness.
Implement a code review process focusing on security. Peer reviews can help catch potential vulnerabilities that a single developer might overlook.
Висновок
Reflected XSS attacks present a notable security risk in web applications, and the canonical link tag can become an unexpected vector for exploitation when user-supplied input is not properly sanitized. Understanding the mechanics of these attacks is critical for developers and security professionals to adequately protect web applications. Implementing robust input validation, output encoding, and regular security audits are essential defenses against these types of vulnerabilities. Security tools and scanners play a pivotal role in identifying potential risks, and continuous education in web security is imperative for maintaining the integrity and confidentiality of user data. By following industry best practices and leveraging the resources and tools available, organizations can better shield themselves from the consequences of XSS vulnerabilities and ensure the safety of their digital environments.
Інші Послуги
Insomnia Security Scanner
AI-powered web application security scanner by CQR. Automated vulnerability discovery, exploit verification, and detailed reporting for modern applications.
Дізнатися більшеЗахист інфраструктури CRYEYE
Аудит безпеки за допомогою CryEye забезпечує інформаційну безпеку підприємства, захищаючи всю інфраструктуру.
Дізнатися більшеТестування на проникнення
Знайдіть вразливості у всій інфраструктурі вашого бізнесу раніше, ніж це зроблять хакери! У межах консалтингу з тестування на проникнення ми підберемо методи пентестів та інші індивідуальні рекомендації з кібербезпеки для вашого бізнесу.
Дізнатися більшеСоціальна Інженерія
Simulate real-world phishing, vishing, and pretexting attacks to measure and improve your team's security awareness and response capabilities.
Дізнатися більшеТестування Продуктивності
Усі види тестування навантаження і продуктивності вашої системи від компанії CQR, що спеціалізується на онлайн-безпеці.
Дізнатися більшеAI-Powered Vulnerability Assessment
Leverage artificial intelligence to discover, prioritize, and remediate vulnerabilities across your digital assets faster and more accurately than traditional scanners.
Дізнатися більшеCloud Security Audit (AWS / GCP / Azure)
Comprehensive security review of your cloud environments — IAM policies, network controls, data exposure, and misconfigurations across all major cloud platforms.
Дізнатися більшеDevSecOps Integration
Embed security into every stage of your CI/CD pipeline. Automated SAST, DAST, SCA, and secret scanning so vulnerabilities are caught before they reach production.
Дізнатися більшеAPI Security Testing
In-depth testing of REST, GraphQL, and SOAP APIs for authentication flaws, authorization bypasses, injection vulnerabilities, and data leakage risks.
Дізнатися більшеMobile Application Penetration Testing
Manual and automated security testing for iOS and Android applications — reverse engineering, runtime analysis, traffic interception, and backend API assessment.
Дізнатися більшеIoT Security Assessment
Evaluate firmware, communication protocols, cloud backends, and physical interfaces of IoT devices to identify vulnerabilities before attackers do.
Дізнатися більшеBlockchain & Smart Contract Audit
Formal verification and manual code review of smart contracts on Ethereum, Solana, and other chains. Detect reentrancy, overflow, and logic flaws before deployment.
Дізнатися більшеRed Team Operations
Advanced adversary simulation using real attacker TTPs (MITRE ATT&CK) to test your detection, response, and overall security posture under realistic conditions.
Дізнатися більшеThreat Intelligence & Monitoring
Continuous monitoring of threat feeds, dark web, and attacker infrastructure to provide actionable intelligence specific to your organization and industry.
Дізнатися більшеZero Trust Architecture Review
Assess and design your Zero Trust security model — identity verification, micro-segmentation, least-privilege access, and continuous validation controls.
Дізнатися більшеCompliance Consulting (PCI DSS / SOC 2 / GDPR)
Expert guidance to achieve and maintain compliance with major security frameworks. Gap analysis, remediation roadmaps, and audit-readiness support.
Дізнатися більшеDark Web Monitoring
Continuous surveillance of dark web forums, marketplaces, and breach databases for leaked credentials, sensitive data, or mentions of your organization.
Дізнатися більшеPhishing Simulation & Awareness Training
Controlled phishing campaigns combined with interactive security awareness training to build a human firewall across your entire organization.
Дізнатися більшеSupply Chain Security Audit
Assess third-party vendor risks, open-source dependencies, and software supply chain integrity to prevent attacks like SolarWinds and Log4Shell.
Дізнатися більшеContainer & Kubernetes Security
Security review of Docker images, Kubernetes clusters, RBAC policies, network policies, and runtime configurations to harden your container infrastructure.
Дізнатися більшеWeb Application Firewall (WAF) Deployment
Professional WAF setup, rule tuning, and ongoing management to block SQL injection, XSS, CSRF, and other OWASP Top 10 threats in real time.
Дізнатися більшеBug Bounty Program Management
Full lifecycle management of your bug bounty program — scope definition, researcher coordination, triage, validation, and remediation tracking.
Дізнатися більшеOSINT Investigation Services
Open-source intelligence gathering on individuals, organizations, and infrastructure. Ideal for pre-engagement recon, fraud investigation, and competitive analysis.
Дізнатися більшеDigital Forensics & Incident Response
Rapid response to security breaches — evidence collection, malware analysis, attacker timeline reconstruction, and actionable remediation recommendations.
Дізнатися більше