EXPLOITING BROKEN ACCESSES CONTROL

A web application uses access control, also known as authorization, to allow some users to access certain content and functionalities while preventing others from doing so. Following authentication, these checks control the actions that “authorized” users are permitted to take. Although access control seems like a straightforward issue, proper implementation is quite challenging. The content and features that a website offers are strongly related to the access control model of that application. Furthermore, users can belong to many roles or groups, each with unique privileges and capabilities.
Broken access control is the application of constraints on who or what is authorized to perform actions or access resources. In the context of web applications, access control is dependent on authentication and session management
Broken access control are frequently malfunctioning and provide a serious security risk. In кібербезпека, Пентест and ethical hacking, this вразливість is quite well known. Broken access control design and administration is a dynamic and complex problem that combines technical implementation with organizational, regulatory, and business limitations. Since humans must make decisions about the design of access controls, there is a great chance for error.
Example of exploitation
In that example we have unprotected admin function
that we can use to access the admin panel and we will using it to delete user
To make that we need to change cookie we need to identifies administrators using a forgeable cookie
To look how cookie sat on that web site we need to log in as regular user
We will do it with Burpsuite
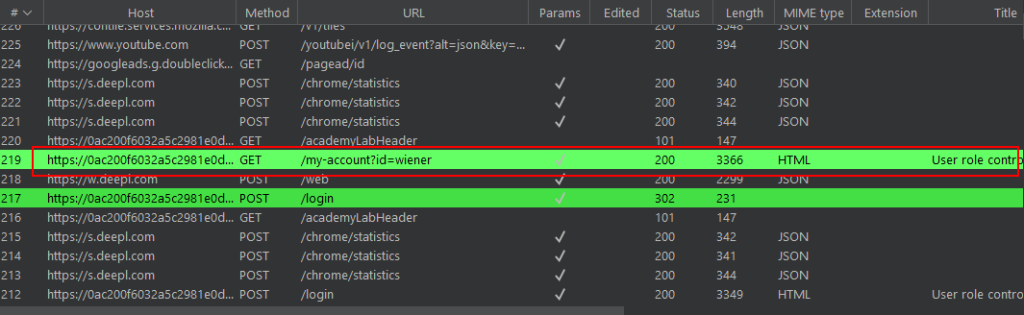
First step we need to log in to our account and capture POST request

We got set a 2 cookie. The 1st cookie is <Set-Cookie: Admin=false; Secure; HttpOnly > admin cookie and 2nd one is a session cookie <session=tAAD6ixIrVTEWC5flYX8Fj6M3chhRqMJ>
The session cookie need to just identify you
However admin cookie is abnormal
It show us that it false but what will be if we set it on =true
So what we going to do – we need to send our /my-account request to the repeater

Then we send that request and try to find admin panel
As we can see we have 0 matches

So we will try to set parameter to =true

And here we got 1 match
Now we need go back to the website and go to >inspector > storage > cookie and change Value – Admin parameter to true
Then we close inspector tab and click on my account

For now Admin panel is appear we click on it and go t burpsuite too

Here we can see that we have successfully deleted user !

Automated Scanners and manual tools for detect that vulnerability
Automated Scanners:
1. Nessus: Nessus is a popular vulnerability scanner that can automatically identify various security issues, including broken access controls.
2. OpenVAS: OpenVAS (Open Vulnerability Assessment System) is an open-source vulnerability scanner that detects security issues, including misconfigured access controls.
3. Nmap: Although primarily a network scanner, Nmap can also detect certain misconfigurations and vulnerabilities related to access controls.
4. Acunetix: Acunetix is a web vulnerability scanner that can identify flaws in web applications, including access control issues.
5. OWASP ZAP (Zed Attack Proxy): ZAP is an open-source web application security scanner that can detect vulnerabilities, including those related to access controls.
Ручні Інструменти:
1. Burp Suite: Burp Suite is a versatile web application testing tool that includes features for manual testing of access control vulnerabilities.
2. Metasploit: Metasploit Framework can be used for manual exploitation of access control vulnerabilities, among other security issues.
3. Sqlmap: Sqlmap is a popular tool for automated SQL injection and database takeover but can also be used to exploit access control weaknesses in web applications.
4. DirBuster: DirBuster is a tool used to discover hidden directories and files on web servers, often revealing areas where access controls might be weak or misconfigured.
5. Manual code review: Manual inspection of source code, configurations, and permissions settings can also uncover access control vulnerabilities that automated tools might miss.
Average CVSS score for broken accesses control
Depending on the particular vulnerabilities being evaluated, the average Common Vulnerability Scoring System (CVSS) score for vulnerabilities relating to failed access controls may change. Broken access control vulnerabilities, on the other hand, are typically regarded as high severity due to their potential to provide unauthorized access to important information or functionality.
A high CVSS score example of a broken access control vulnerability is “Insecure Direct Object References (IDOR).” When a program exposes internal implementation objects—like files, directories, or database keys—to users without conducting the necessary authorization checks, a vulnerability results. This vulnerability can be used by attackers to gain unauthorized access to data or carry out unlawful operations.
Let’s take an example of a web application. Users can view their own profile images by going to URLs such as example.com/profiles//picture (for example). An attacker can alter the URL to access other users’ profile images if the application does not verify that the verified user is authorized to view the picture linked to the provided user_id. There is an IDOR vulnerability here.
A vulnerability of this kind would probably have a high CVSS score, usually between 7.0 and 9.0 or even higher. This high score indicates how serious the vulnerability is, as it may allow unauthorized parties to access private user information and jeopardize the application’s confidentiality and integrity.
CVES related to broken accesses control
CVE-2019-6340: The content management system Drupal has a vulnerability related to this CVE that could allow arbitrary PHP code execution due to inadequate access restriction.
CVE-2020-14882: Improper access control is the root cause of this CVE, which affects Oracle WebLogic Server and may provide unauthorized access to confidential information or functionalities.
CVE-2020-3452: This CVE involves a vulnerability in Cisco Adaptive Security Appliance (ASA) Software that could allow an unauthenticated, remote attacker to view sensitive files on the targeted system due to improper access controls.
CVE-2021-44228: This CVE affects Apache Log4j 2, a popular Java-based logging framework. It was caused by improper access controls in the JNDI feature, leading to remote code execution.
These CVEs highlight how crucial it is to fix faulty access controls in a variety of programs and systems in order to stop unwanted access and possible hostile actor exploitation.
Checklist
1. Access Control Matrix Review: Review the access control matrix to ensure that permissions are assigned based on the principle of least privilege.
Verify that users only have access to the resources and functionalities they need to perform their tasks.
2. Authentication Mechanisms: Ensure strong authentication mechanisms are in place, such as multi-factor authentication (MFA), to prevent unauthorized access.
Validate the effectiveness of password policies, including complexity requirements and regular password rotation.
3. Session Management: Review session management mechanisms to prevent session fixation, session hijacking, and session timeout issues.
Ensure that sessions are securely managed and terminated after a reasonable period of inactivity.
4. URL and Object References: Check for insecure direct object references (IDOR) by reviewing URLs, parameters, and object references.
Implement proper authorization checks to prevent unauthorized access to sensitive resources.
5. Error Handling: Implement secure error handling mechanisms to avoid leaking sensitive information, such as stack traces or error messages, to unauthorized users.
6. API Security: Secure APIs by implementing proper authentication and authorization mechanisms, such as OAuth or API keys.
Validate user input and enforce access controls on API endpoints to prevent misuse or abuse.
7. File and Directory Permissions: Review file and directory permissions to ensure that sensitive files are not accessible to unauthorized users.
Implement file and directory access controls based on user roles and responsibilities.
8. Testing and Monitoring: Conduct regular security testing, including penetration testing and vulnerability scanning, to identify and address access control vulnerabilities.
Implement logging and monitoring mechanisms to detect and respond to unauthorized access attempts in real-time.
9. Security Awareness Training: Provide security awareness training to users and developers to educate them about the importance of access control and best practices for maintaining secure access controls.
10. Compliance and Regulations: Ensure compliance with relevant regulations and standards, such as GDPR, HIPAA, or PCI DSS, which may include specific requirements for access control measures.
Books and courses to study more about broken accesses control
Книги:
1. “The Web Application Hacker’s Handbook: Finding and Exploiting Security Flaws” by Dafydd Stuttard and Marcus Pinto: This book covers web application security flaws in great detail, including issues with broken access control, and it gives helpful advice on how to find and fix these problems.
2. “OWASP Testing Guide v4” by OWASP (Open Web Application Security Project): This tutorial provides useful approaches and strategies for locating and fixing vulnerabilities, as well as covering a variety of topics related to web application security testing, such as faulty access control.
3. “Hacking: The Art of Exploitation” by Jon Erickson: Although not explicitly addressing access control, this book offers insightful information about the mindset and methods attackers employ to take advantage of weaknesses, including malfunctioning access controls.
Курси:
1. OWASP Top 10: Web Application Security Risks: Breaking access control is one of the top security concerns identified in the OWASP Top 10, which is the subject of several online courses. The detection, exploitation, and mitigation techniques for a variety of vulnerabilities are covered in these courses.
2. Cybrary – Web Application Penetration Testing: Web application penetration testing is covered in detail in a thorough course by Cybrary, which addresses issues like session management vulnerabilities, broken access control, and authentication bypass.
3. Pluralsight – Web Security and OWASP Top 10: Broken access control and related concerns are covered in modules of Pluralsight’s web security and OWASP Top 10 courses.
4. Udemy – Ethical Hacking and Web Application Penetration Testing: A variety of courses on online application penetration testing and ethical hacking are available on Udemy. These courses include methods for locating and taking advantage of broken access control vulnerabilities.
5. Coursera – Web Security Fundamentals: Web security fundamentals courses are available on Coursera. These courses include case studies, practical exercises, and coverage of issues including authorization mechanisms, authentication, and access control.
Висновок
In summary, compromised access control is a serious security risk that can result in unwanted access to private information or system functionality. It happens when access controls are not appropriately put into place, giving attackers the ability to get around authentication restrictions, increase their level of privilege, or access things they are not supposed to. Organizations must place a high priority on implementing strong access control methods, such as appropriate session management, authentication, and authorization, in order to effectively address broken access control vulnerabilities. This entails applying the least privilege principle, which states that users should only be given the minimal amount of access required to do their duties. Proactively identifying and mitigating access control concerns also requires regular security testing, monitoring, and user training. Organizations can lower the risk of unauthorized access and shield their systems and data from hostile actors by giving access control measures top priority and being on the lookout for potential vulnerabilities.
Інші Послуги
Insomnia Security Scanner
AI-powered web application security scanner by CQR. Automated vulnerability discovery, exploit verification, and detailed reporting for modern applications.
Дізнатися більшеЗахист інфраструктури CRYEYE
Аудит безпеки за допомогою CryEye забезпечує інформаційну безпеку підприємства, захищаючи всю інфраструктуру.
Дізнатися більшеТестування на проникнення
Знайдіть вразливості у всій інфраструктурі вашого бізнесу раніше, ніж це зроблять хакери! У межах консалтингу з тестування на проникнення ми підберемо методи пентестів та інші індивідуальні рекомендації з кібербезпеки для вашого бізнесу.
Дізнатися більшеСоціальна Інженерія
Simulate real-world phishing, vishing, and pretexting attacks to measure and improve your team's security awareness and response capabilities.
Дізнатися більшеТестування Продуктивності
Усі види тестування навантаження і продуктивності вашої системи від компанії CQR, що спеціалізується на онлайн-безпеці.
Дізнатися більшеAI-Powered Vulnerability Assessment
Leverage artificial intelligence to discover, prioritize, and remediate vulnerabilities across your digital assets faster and more accurately than traditional scanners.
Дізнатися більшеCloud Security Audit (AWS / GCP / Azure)
Comprehensive security review of your cloud environments — IAM policies, network controls, data exposure, and misconfigurations across all major cloud platforms.
Дізнатися більшеDevSecOps Integration
Embed security into every stage of your CI/CD pipeline. Automated SAST, DAST, SCA, and secret scanning so vulnerabilities are caught before they reach production.
Дізнатися більшеAPI Security Testing
In-depth testing of REST, GraphQL, and SOAP APIs for authentication flaws, authorization bypasses, injection vulnerabilities, and data leakage risks.
Дізнатися більшеMobile Application Penetration Testing
Manual and automated security testing for iOS and Android applications — reverse engineering, runtime analysis, traffic interception, and backend API assessment.
Дізнатися більшеIoT Security Assessment
Evaluate firmware, communication protocols, cloud backends, and physical interfaces of IoT devices to identify vulnerabilities before attackers do.
Дізнатися більшеBlockchain & Smart Contract Audit
Formal verification and manual code review of smart contracts on Ethereum, Solana, and other chains. Detect reentrancy, overflow, and logic flaws before deployment.
Дізнатися більшеRed Team Operations
Advanced adversary simulation using real attacker TTPs (MITRE ATT&CK) to test your detection, response, and overall security posture under realistic conditions.
Дізнатися більшеThreat Intelligence & Monitoring
Continuous monitoring of threat feeds, dark web, and attacker infrastructure to provide actionable intelligence specific to your organization and industry.
Дізнатися більшеZero Trust Architecture Review
Assess and design your Zero Trust security model — identity verification, micro-segmentation, least-privilege access, and continuous validation controls.
Дізнатися більшеCompliance Consulting (PCI DSS / SOC 2 / GDPR)
Expert guidance to achieve and maintain compliance with major security frameworks. Gap analysis, remediation roadmaps, and audit-readiness support.
Дізнатися більшеDark Web Monitoring
Continuous surveillance of dark web forums, marketplaces, and breach databases for leaked credentials, sensitive data, or mentions of your organization.
Дізнатися більшеPhishing Simulation & Awareness Training
Controlled phishing campaigns combined with interactive security awareness training to build a human firewall across your entire organization.
Дізнатися більшеSupply Chain Security Audit
Assess third-party vendor risks, open-source dependencies, and software supply chain integrity to prevent attacks like SolarWinds and Log4Shell.
Дізнатися більшеContainer & Kubernetes Security
Security review of Docker images, Kubernetes clusters, RBAC policies, network policies, and runtime configurations to harden your container infrastructure.
Дізнатися більшеWeb Application Firewall (WAF) Deployment
Professional WAF setup, rule tuning, and ongoing management to block SQL injection, XSS, CSRF, and other OWASP Top 10 threats in real time.
Дізнатися більшеBug Bounty Program Management
Full lifecycle management of your bug bounty program — scope definition, researcher coordination, triage, validation, and remediation tracking.
Дізнатися більшеOSINT Investigation Services
Open-source intelligence gathering on individuals, organizations, and infrastructure. Ideal for pre-engagement recon, fraud investigation, and competitive analysis.
Дізнатися більшеDigital Forensics & Incident Response
Rapid response to security breaches — evidence collection, malware analysis, attacker timeline reconstruction, and actionable remediation recommendations.
Дізнатися більше