Security Awareness Staff Training

Introduction to Security Awareness Staff Training
Nowadays most people think they have a good knowledge of cyber hygiene, but statistics show that it is much easier to attack humans than systems or applications, because not everyone is as knowledgeable as they think. Unlike machines, people can make mistakes.
However, hackers are constantly developing their skills and finding more and more new sophisticated ways of attacking, so now even experienced and knowledgeable employees can fall into their trap. In order to prevent this from happening, security training and education of both novice and more experienced employees should be conducted at least once a year. The information security team needs to keep up with all the changes in the world of hacking in order to respond quickly to new attack methods, integrate new approaches to security, and train employees to be prepared for all new threats. The security training itself should always be based on real attack simulations that are in line with the latest criminal trends.
Every year new threats appear, new malware is coded, and new phishing schemes are developed. If your team is unaware of these changes and unprepared to handle them, the risk of a successful attack increases until an attack becomes inevitable.
Security awareness training of employees is required both to pass the audit of the company during the certification session, such as SOC 2 certification, and just to eliminate the possibility of attacks such as phishing or social engineering, as a consequence of which the company can get a large financial loss.
Don’t skimp on this investment, as it may be the most important decision you can make to ensure the safety and stability of your business.
The price of awareness will vary depending on the desired result, for example if you need to prepare for certification – will have to hire a separate team to professionally assess the security of personnel, by conducting red team operations in which all vectors of attack will be tested from checking the awareness of office guards, ending with the company leaders.
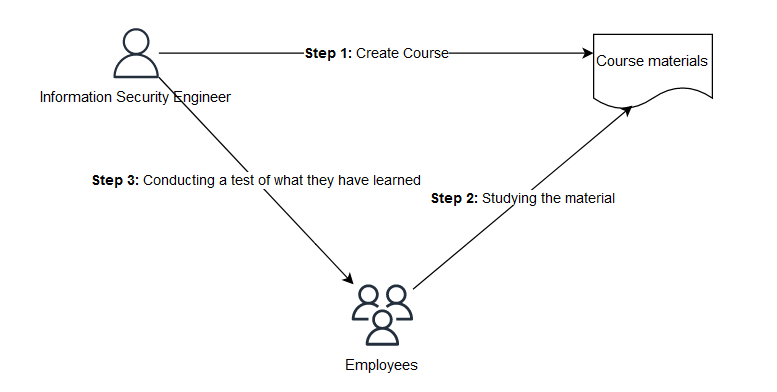
Usually, such trainings are conducted by the team responsible for information security, providing training materials with various examples of attack implementation, checking the learning of materials in practice by simulating a real case. Employees go through the training material until they have fully absorbed it.

Topics that should be covered in cyber security training
1. Phishing as a part of social engineering is a type of Internet fraud whose main purpose is to gain access to users confidential data – logins (username or email) and passwords. By spoofing the official site in order to intercept valuable information.
To avoid such an attack, you need to pay attention to the accounts of users sending you messages and their content, namely links, because the essence of phishing attacks is to enter their data on a fake site.
For example, the official domain of Facebook, will be facebook.com, in case we want to go to our page we will have such a path https://www.facebook.com/login, but if we will be sent a phishing, it will be different from the official domain, having this form https://www.faceboook.com/login.
In the case of users, you need to pay attention to which email was sent from and, accordingly, the name of the sender.
For example, we can expect an email from John Baker from gmail. The official account will be [email protected], but when phishing we will see [email protected] or [email protected].
2. Password security – the essence of this problem is the neglect of employees to create strong or new non-repeatable passwords.
It is to avoid such cases that employees should be trained and made aware of the importance of all safety measures.
The presence of weak passwords leads to their picking or as among hackers, this method is called bruteforce.
If, however, the password is repeated in its entirety, then when a company leaks or maybe that password was used on external resources that had leaks, they can be repeated by intruders in order to gain profit.
If the password is partially repeated, it will be possible to match this password with a mask, and thus speed up the process of bruteforce.
3. Privacy issues – the essence of this problem is that employees may be negligent with critical data.
To solve this problem, you need to train employees how to store and use this data, namely, not to store it on personal drives (flash drive, for example), not to transmit them over an insecure channel and store this data in encrypted form.
4. Compliance is about complying with requirements such as the well-known GDPR, HIPAA, PCI.
It is important that employees adhere to the general rules that meet these requirements, they must know what it is and how it affects them personally.
5. Insider threats – this term describes the introduction into your company of an employee from a competitor’s company who may carry out various spying activities there.
It is important to teach employees to respond to excessive interest from internal employees to data they should not be interested in. For example, an employee from the human resources department rubs off on the developers and tries to get information from them about secret projects or blueprints.
6. CEO/wire fraud – very often attackers pretend to be in charge of the company in order to influence employees or get sensitive data from them.
It is important to teach employees to study the request from the leaders of the company and not to trust them 100%, it is better to contact and ask again than to give out secret information to a potentially fake director.
7. Office hygiene – being in the office you can’t always be sure that your data or device is safe.
We need to teach employees what to do in the office, which is not to leave your device open (not locked) or leave it in places where no one can see it, such as places where there are no cameras or people. As we already know from previous attack vectors, there could be spies inside the company who would be happy to find such a device and infect it with a virus or just steal data.
9. Hygiene when working remotely – against the backdrop of recent events, this has become especially relevant, a situation like to hygiene in the office, only outside the office.
Here, even more attention should be paid to the issue of security, your device should always be in your sight. It is also not recommended to look at sensitive data in public places and go under the public Wifi, even if you just need to send an e-mail, this is fraught with the fact that it can be intercepted by intruders.
Заключение
In conclusion, employee security awareness is a very important part of a company’s security strategy, because it is a fundamental level of defense. You can have the latest technology for security, but it can’t handle the fact that users themselves will inadvertently hand over data to intruders.
Our social engineering as a service {https://cqr.company/service/social-engineering/}, involves all phases of awareness assessment, from modeling, conducting a social engineering type attack, generating reports and providing recommendations for staff training.
Другие Услуги
Insomnia Security Scanner
AI-powered web application security scanner by CQR. Automated vulnerability discovery, exploit verification, and detailed reporting for modern applications.
Узнать большеЗащита Инфраструктуры CRYEYE
Аудит безопасности с помощью CryEye обеспечивает информационную безопасность предприятия, защищая всю инфраструктуру.
Узнать большеТестирование на проникновение
Найдите уязвимости во всей инфраструктуре вашего бизнеса раньше, чем это сделают хакеры! В рамках консалтинга по тестированию на проникновение мы подберем методы пентестов.
Узнать большеСоциальная инженерия
Simulate real-world phishing, vishing, and pretexting attacks to measure and improve your team's security awareness and response capabilities.
Узнать большеНагрузочное Тестирование
All kinds of load and performance testing of your system from the CQR online security company.
Узнать большеAI-Powered Vulnerability Assessment
Leverage artificial intelligence to discover, prioritize, and remediate vulnerabilities across your digital assets faster and more accurately than traditional scanners.
Узнать большеCloud Security Audit (AWS / GCP / Azure)
Comprehensive security review of your cloud environments — IAM policies, network controls, data exposure, and misconfigurations across all major cloud platforms.
Узнать большеDevSecOps Integration
Embed security into every stage of your CI/CD pipeline. Automated SAST, DAST, SCA, and secret scanning so vulnerabilities are caught before they reach production.
Узнать большеAPI Security Testing
In-depth testing of REST, GraphQL, and SOAP APIs for authentication flaws, authorization bypasses, injection vulnerabilities, and data leakage risks.
Узнать большеMobile Application Penetration Testing
Manual and automated security testing for iOS and Android applications — reverse engineering, runtime analysis, traffic interception, and backend API assessment.
Узнать большеIoT Security Assessment
Evaluate firmware, communication protocols, cloud backends, and physical interfaces of IoT devices to identify vulnerabilities before attackers do.
Узнать большеBlockchain & Smart Contract Audit
Formal verification and manual code review of smart contracts on Ethereum, Solana, and other chains. Detect reentrancy, overflow, and logic flaws before deployment.
Узнать большеRed Team Operations
Advanced adversary simulation using real attacker TTPs (MITRE ATT&CK) to test your detection, response, and overall security posture under realistic conditions.
Узнать большеThreat Intelligence & Monitoring
Continuous monitoring of threat feeds, dark web, and attacker infrastructure to provide actionable intelligence specific to your organization and industry.
Узнать большеZero Trust Architecture Review
Assess and design your Zero Trust security model — identity verification, micro-segmentation, least-privilege access, and continuous validation controls.
Узнать большеCompliance Consulting (PCI DSS / SOC 2 / GDPR)
Expert guidance to achieve and maintain compliance with major security frameworks. Gap analysis, remediation roadmaps, and audit-readiness support.
Узнать большеDark Web Monitoring
Continuous surveillance of dark web forums, marketplaces, and breach databases for leaked credentials, sensitive data, or mentions of your organization.
Узнать большеPhishing Simulation & Awareness Training
Controlled phishing campaigns combined with interactive security awareness training to build a human firewall across your entire organization.
Узнать большеSupply Chain Security Audit
Assess third-party vendor risks, open-source dependencies, and software supply chain integrity to prevent attacks like SolarWinds and Log4Shell.
Узнать большеContainer & Kubernetes Security
Security review of Docker images, Kubernetes clusters, RBAC policies, network policies, and runtime configurations to harden your container infrastructure.
Узнать большеWeb Application Firewall (WAF) Deployment
Professional WAF setup, rule tuning, and ongoing management to block SQL injection, XSS, CSRF, and other OWASP Top 10 threats in real time.
Узнать большеBug Bounty Program Management
Full lifecycle management of your bug bounty program — scope definition, researcher coordination, triage, validation, and remediation tracking.
Узнать большеOSINT Investigation Services
Open-source intelligence gathering on individuals, organizations, and infrastructure. Ideal for pre-engagement recon, fraud investigation, and competitive analysis.
Узнать большеDigital Forensics & Incident Response
Rapid response to security breaches — evidence collection, malware analysis, attacker timeline reconstruction, and actionable remediation recommendations.
Узнать больше